Twelve modules, one data model
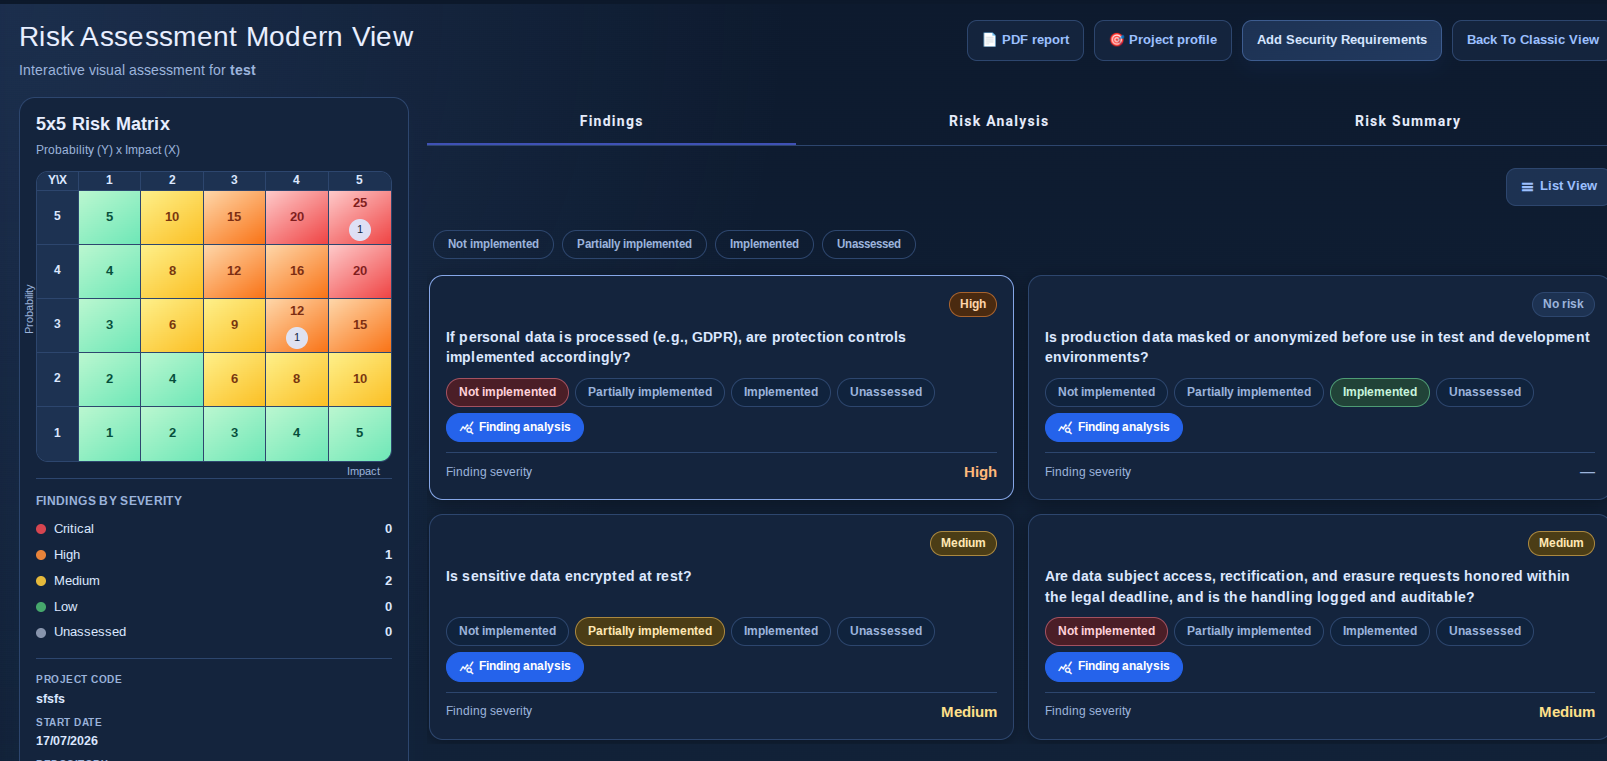
Answer the requirement, get the risk
A 5×5 matrix populated live as findings are scored, finding-level analysis from control gap to rated severity, and a per-project PDF report in one click.

Full lifecycle, fully traceable
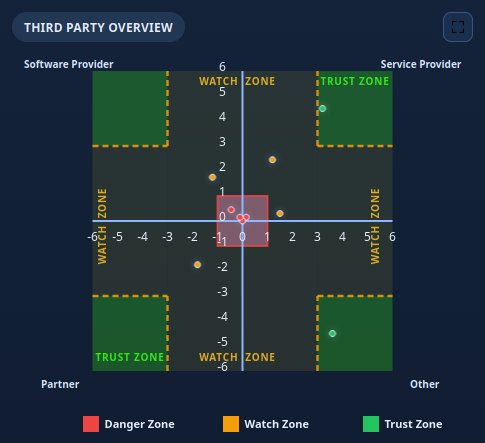
The risk you inherit from your suppliers

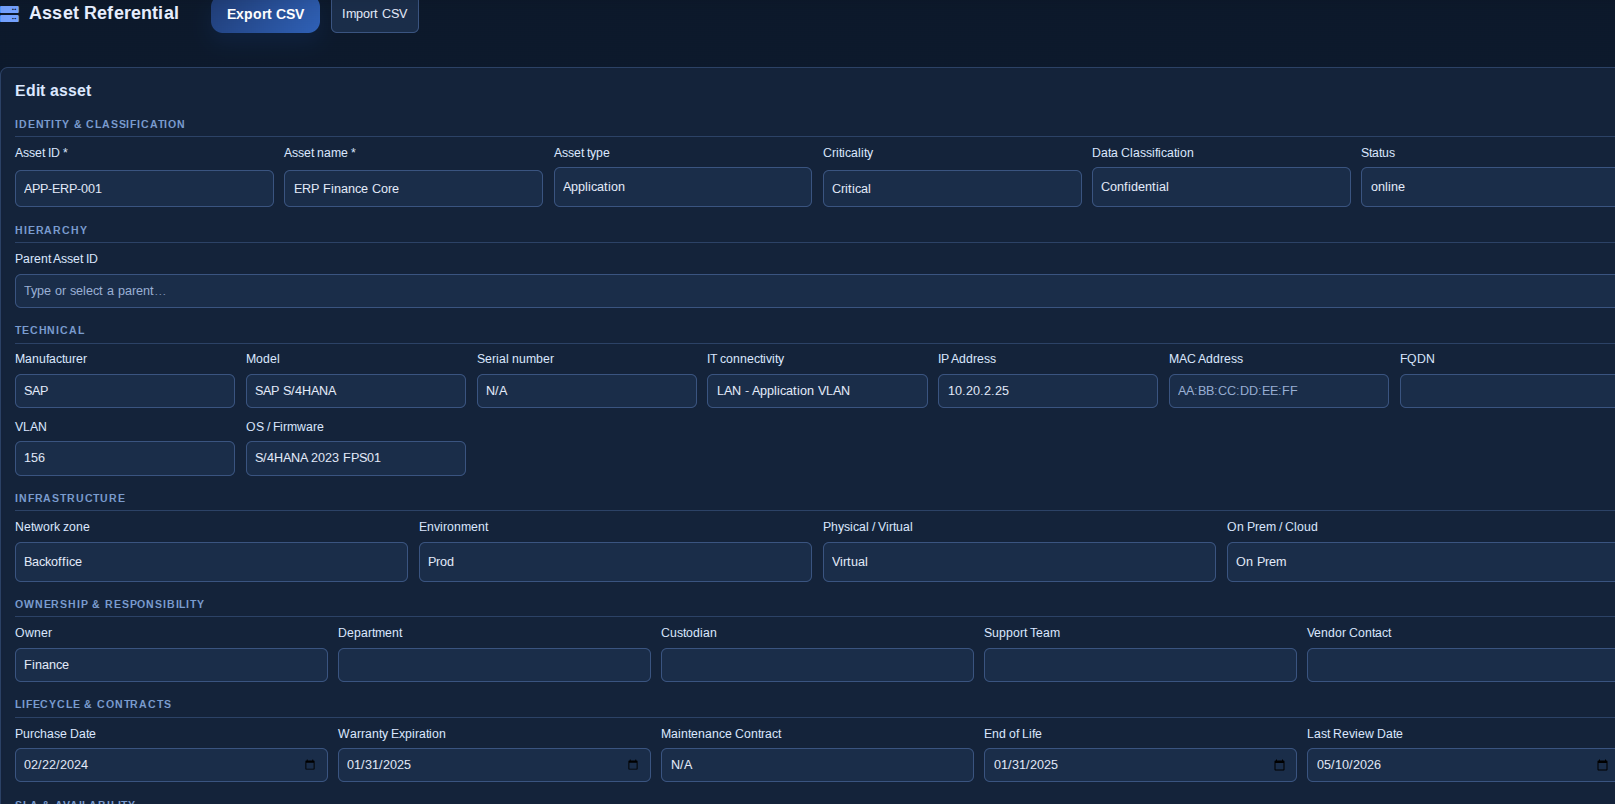
Every register, connected


Two independent stacks, no shared gateway
FETCH & PUSH
GATEWAY
SynapseRM initiates every exchange: it fetches supplier assessment results and pushes back what the portal needs. The portal never calls in, so a compromise on the supplier-facing side does not open a path into the risk platform.
Segregation of duties between security, procurement, DPO and management.
Multi-factor authentication on every account, including supplier access.
Timestamped records of every action, assessment and approval.
A read-only profile so your auditor reads the evidence directly.
Where SynapseRM sits
Take the presentation with you
A 16-slide PDF covering the regulatory context (NIS2, DORA, ISO 27001), the twelve modules, the automated project assessment, TPRM and the architecture, ready to share with your team or your committee.
See it on your own scope
Book a demo, or ask for a test tenant pre-filled with demonstration data.
A Belgium-based provider of cybersecurity solutions, and the team behind SynapseRM / TPRM.